AI Security Services & Solutions
One product and two service pillars: Arcitix Warden governs what your agents are allowed to do, and our practice covers everything either side of that line.
Arcitix Warden
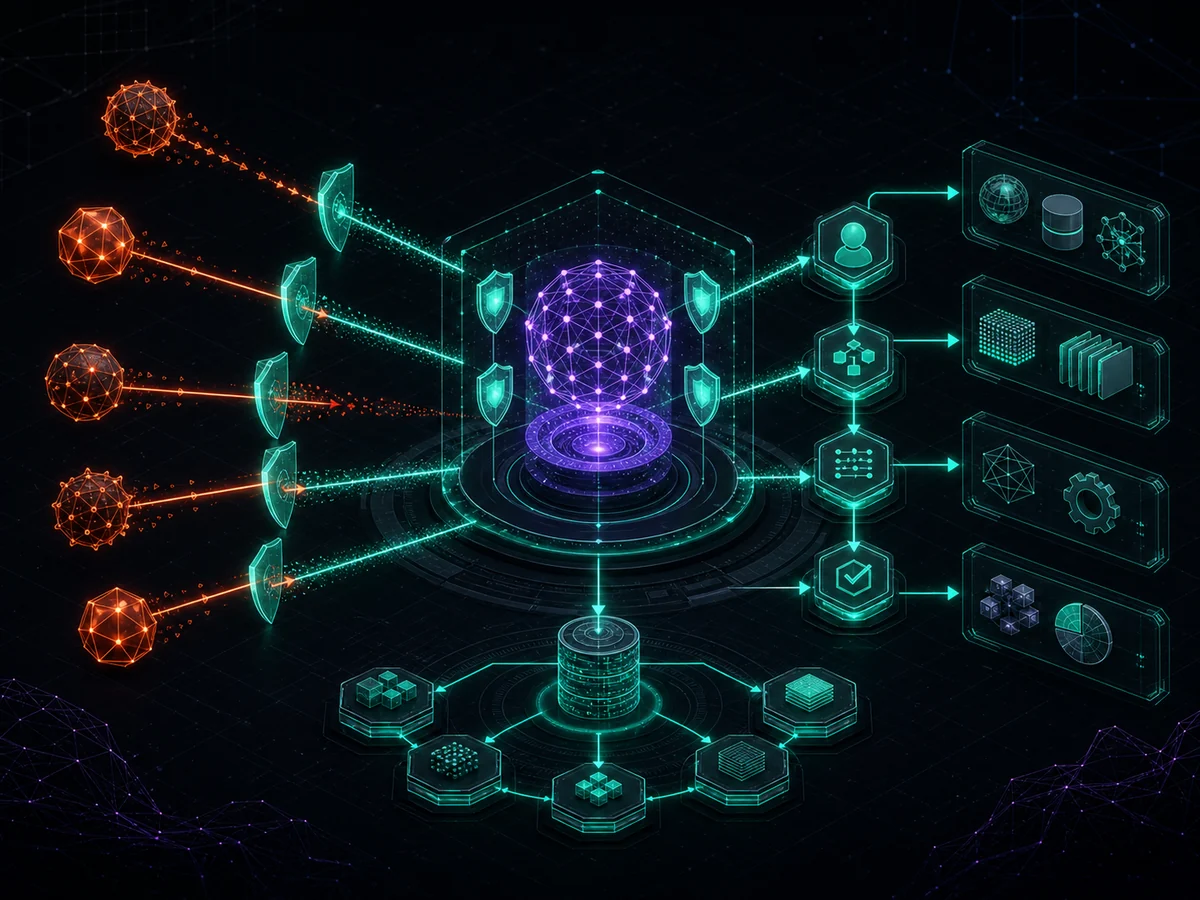
A control plane that sits between your AI agents and the tools and data they can reach. Every tool call carries an identity, clears a policy, and leaves a signed audit record — allowed, held for a human, or blocked, in under fifteen milliseconds.
- Agent identity — workload identity and short-lived credentials per agent
- Action authorization — data-class scope, spend caps, blast-radius limits
- Inline guard models — injection, behavioural drift and PII detection on every call
- Tamper-evident ledger — replayable evidence mapped to NIST AI RMF and the EU AI Act
Warden is pre-launch. We are taking a small number of design partners already running agents with write access in production. The services below are available today and are delivered by the same team.
Defend With AI
AI-powered detection and response that operates at machine speed, with humans in the loop for the decisions that matter.
Agentic Security Operations
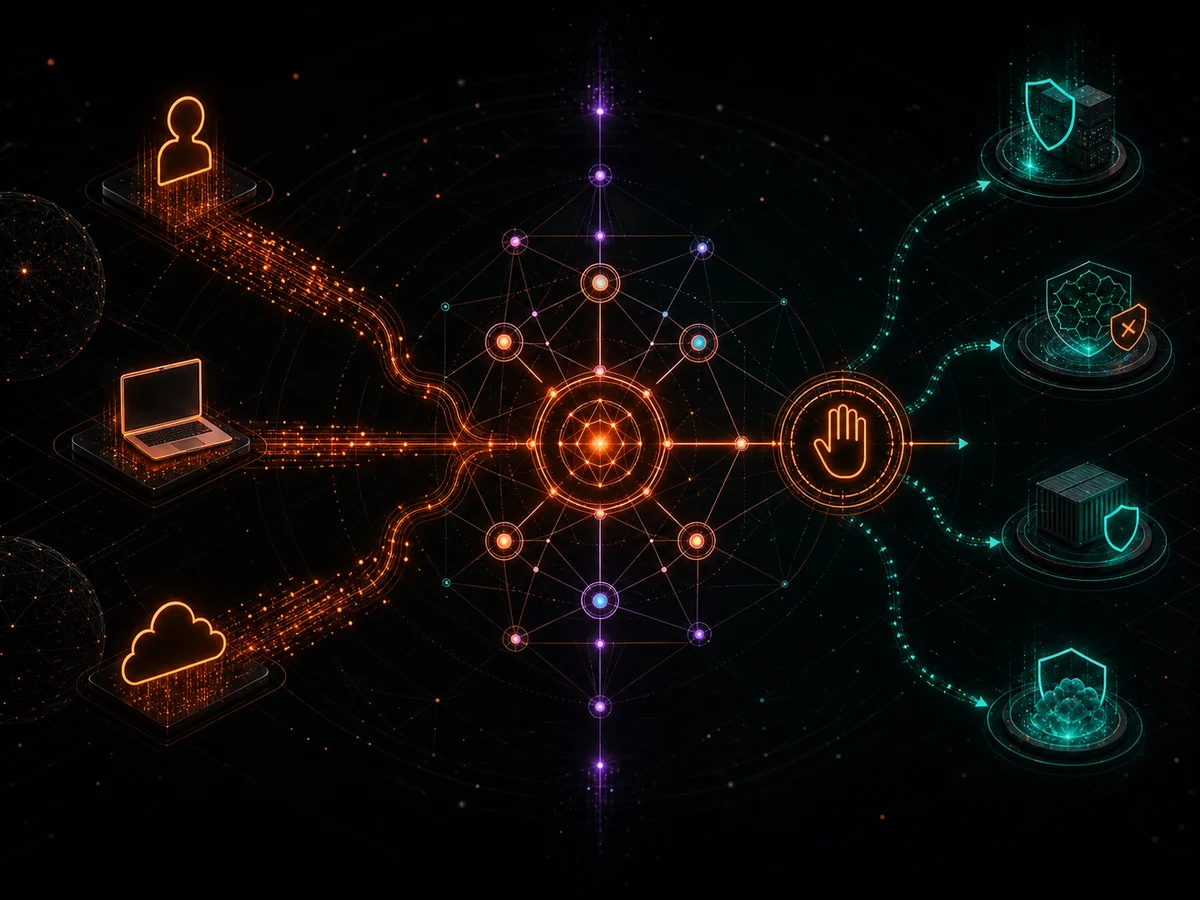
An AI-driven operations layer that correlates signals across identity, endpoint, and cloud, triages alerts, and executes containment playbooks autonomously. Analysts stay in the loop for high-impact decisions while the routine work runs itself.
ML-Driven Threat Detection
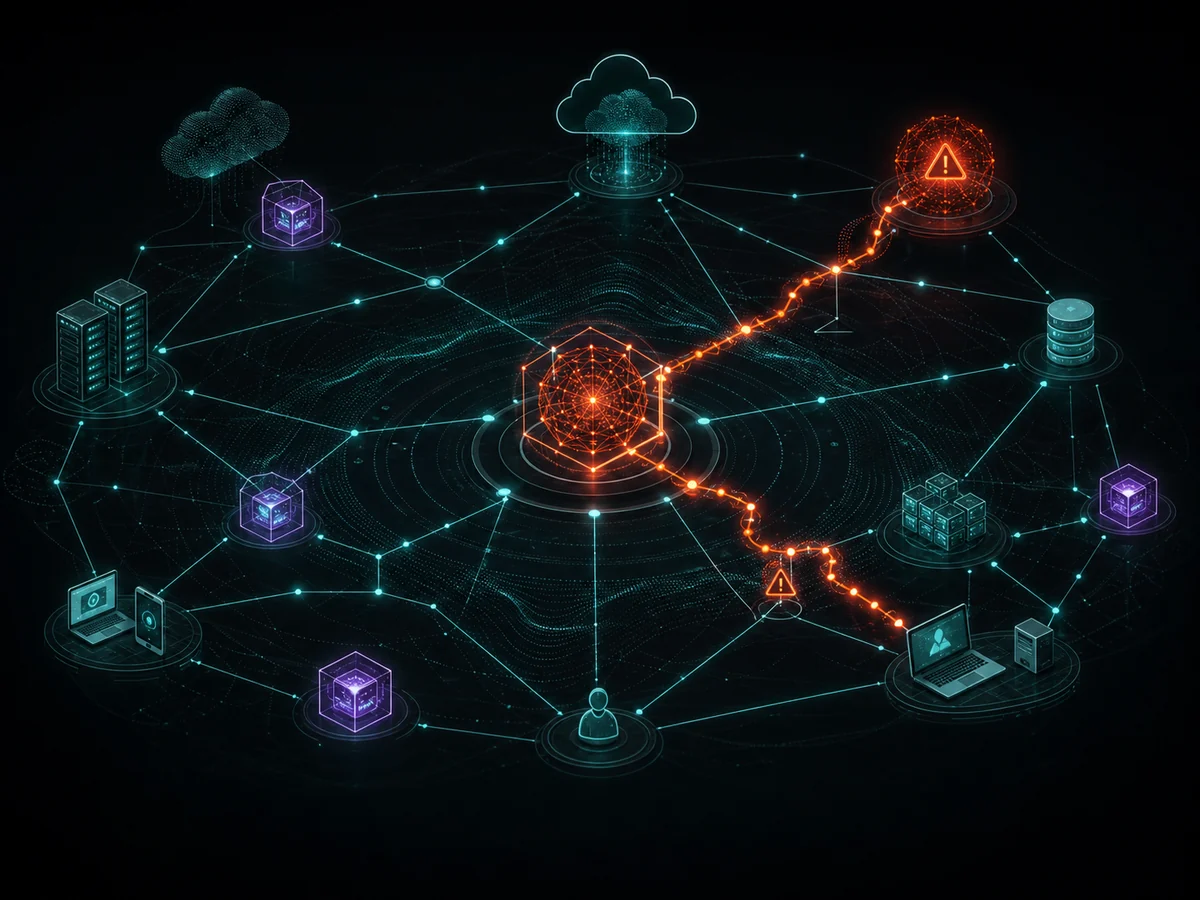
Machine-learning models that profile normal behavior across users, devices, and workloads, then surface the anomalies and novel attack patterns that signature-based tools miss. Less noise, fewer false positives, and earlier warning on real threats.
Accelerated Incident Response
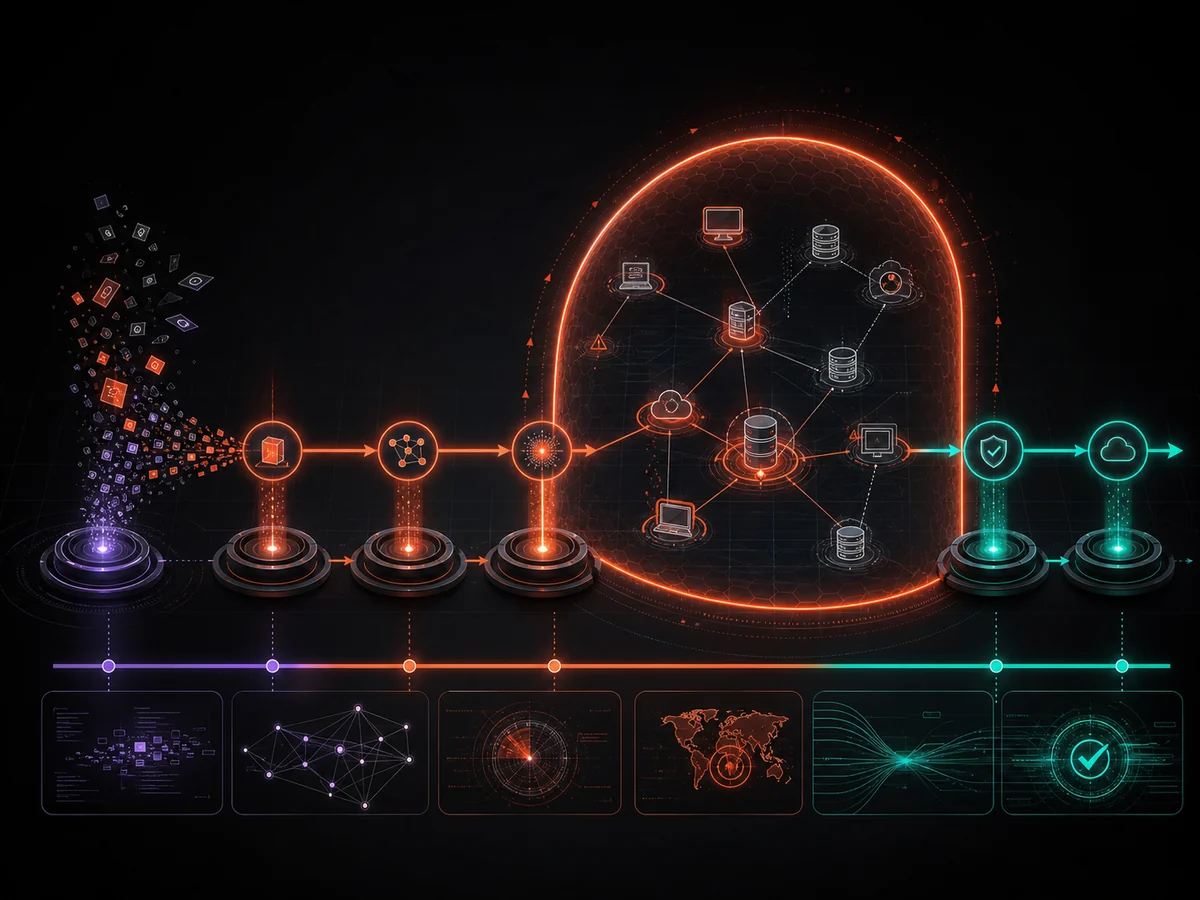
Automated evidence collection, root-cause reconstruction, and guided containment that compress investigation time from days to minutes. When a signal becomes an incident, your team gets a clear timeline, scope, and next steps — not a pile of raw logs.
Secure Your AI
The AI systems you build are a new attack surface. We defend your models, prompts, agents, and training data before attackers exploit them.
LLM Firewall & Guardrails
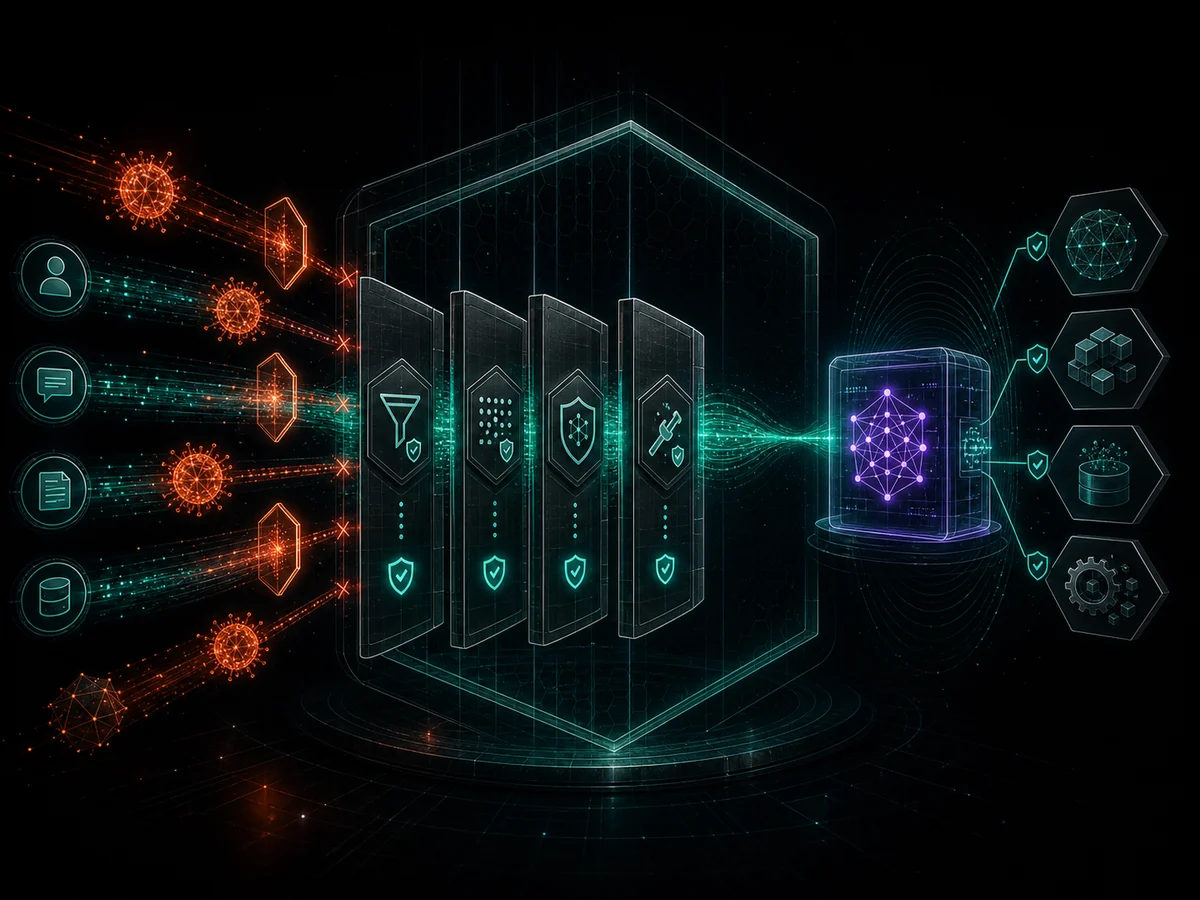
Inline protection for your AI applications and agents. We filter prompt injection and jailbreak attempts, moderate model output, prevent PII and secret leakage, and enforce authorization on the tools and data your agents can reach.
AI & LLM Red Teaming
Adversarial testing of your models and agents the way real attackers operate — jailbreaks, prompt injection, data exfiltration, and multi-step abuse chains. Every finding maps to the OWASP Top 10 for LLM Applications and MITRE ATLAS, with concrete remediation guidance.
AI Governance & Model Risk
Turn "we should govern our AI" into a real program. We build a model inventory, secure your AI supply chain against poisoned data and dependencies, and map evidence to the NIST AI RMF and EU AI Act so your AI initiatives survive audit and board scrutiny.
How We Secure You
A proven methodology spanning both pillars — defending with AI and securing your AI.
Assess
We map your environment and your AI footprint — models, agents, data flows, and the threats that target each.
Red Team
We attack the way adversaries do — across your defenses and your AI systems — to prove what's actually exploitable.
Deploy
We stand up AI-driven detection and LLM guardrails that integrate with your stack and workflows.
Operate
Our agentic SOC runs continuously, hunting threats and containing incidents with analysts on call.
Go deeper on AI security
Practical guides from the Arcitix research team on the threats these services defend against.
What Is an LLM Firewall? Defending GenAI Apps from Prompt Injection
An LLM firewall sits between users and your model to filter malicious prompts and unsafe outputs. Here is what it does, how it works, and where it fits in a defense-in-depth strategy.
AI Red Teaming: A Practical Guide to Breaking Your Own Models
AI red teaming probes your models and agents the way real attackers will. Learn what to test, how to structure a campaign, and how to turn findings into durable defenses.
Building an Agentic SOC: How AI Agents Triage Alerts at Machine Speed
Alert fatigue is breaking traditional SOCs. An agentic SOC uses AI agents to triage, investigate, and contain threats with humans in the loop. Here is how the architecture works.
Securing RAG Pipelines: Threats and Defenses for Retrieval-Augmented Generation
RAG grounds LLMs in your data — and introduces a fresh attack surface. Learn the threats unique to retrieval-augmented generation and how to secure each stage of the pipeline.
The NIST AI Risk Management Framework: A Practical Implementation Guide
The NIST AI RMF gives organizations a structured way to manage AI risk. This guide breaks down its four functions — Govern, Map, Measure, Manage — into actions you can take now.
Shadow AI: Discovering and Governing Unsanctioned AI in the Enterprise
Employees are already using AI tools your security team never approved. Learn how shadow AI creates risk and how to bring it under governance without killing productivity.
Ready to Strengthen Your AI Security?
Request a scoped assessment and receive clear findings, owners, severity rationale, and a remediation roadmap across both pillars.
Request Assessment